

Entry posted by rspstoplist in RSPS ·
2,176 views
ReasonPS source leak and server security
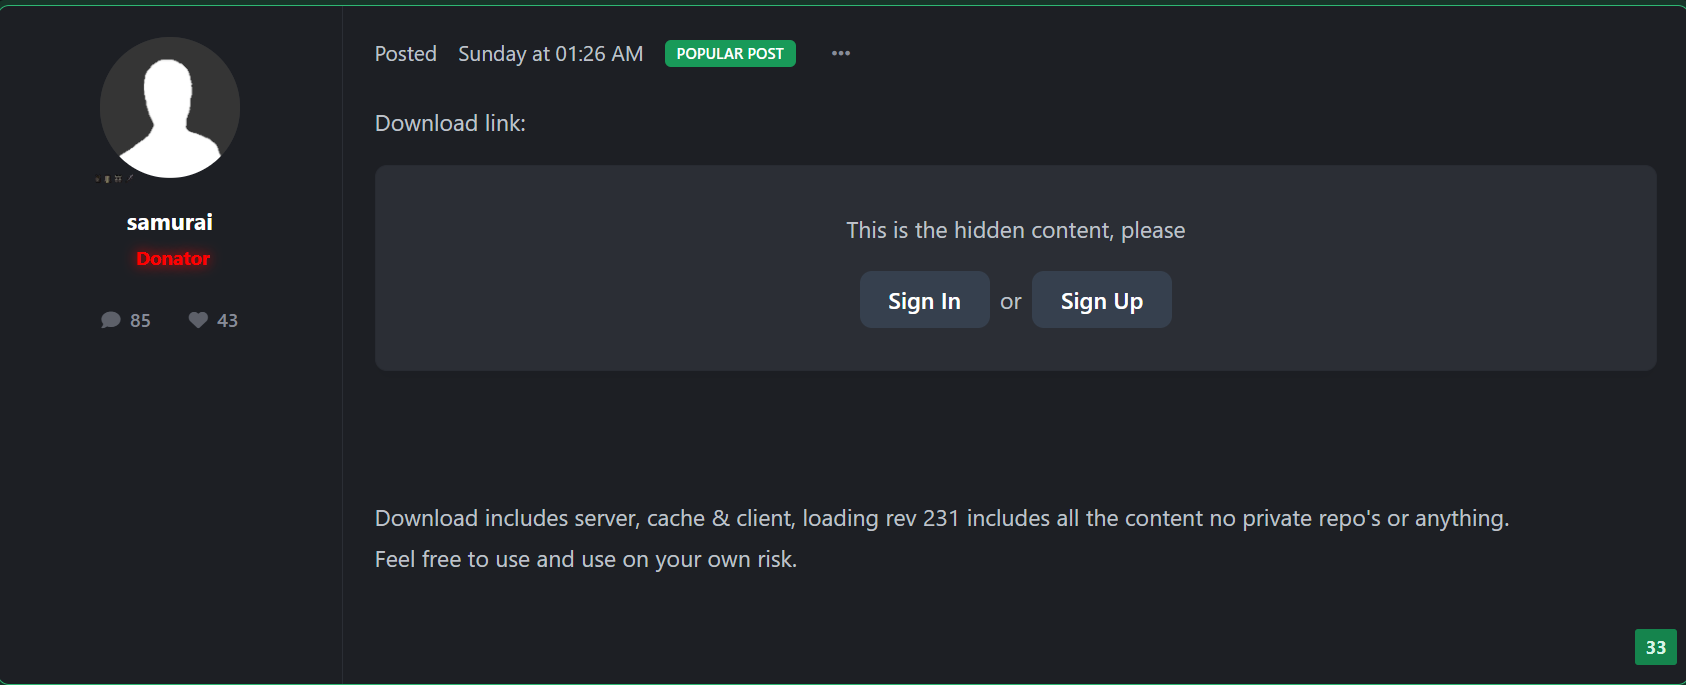
ReasonPS's source code has reportedly leaked. The project used a base derived from Runite/Kronos, a common framework in the RSPS scene.
The leak raises questions about developer access and server security.
What ReasonPS offered
ReasonPS is an OSRS-style server aimed at players who prefer less grinding than in Old School RuneScape.
Its features included:
-
500+ real concurrent players during peak times
-
Custom end-game systems like Royal Titans and Echo Bosses (Raids 4)
-
Fully integrated RuneLite client with HD plugins
-
Continuous updates (50+ logs within 6 months)
-
Custom bosses like Yama, Huey, and DT2 content
It promoted long-term account progression with a reduced grind.
What is known about the source leak
While full technical details are still emerging, internal discussions suggest:
-
The source was based on a Runite/Kronos framework
-
The leak may have originated from a developer identified as “Glabay,” whose Discord handle has been referenced in community discussions.
-
The breach appears to be internal, rather than a direct external exploit
-
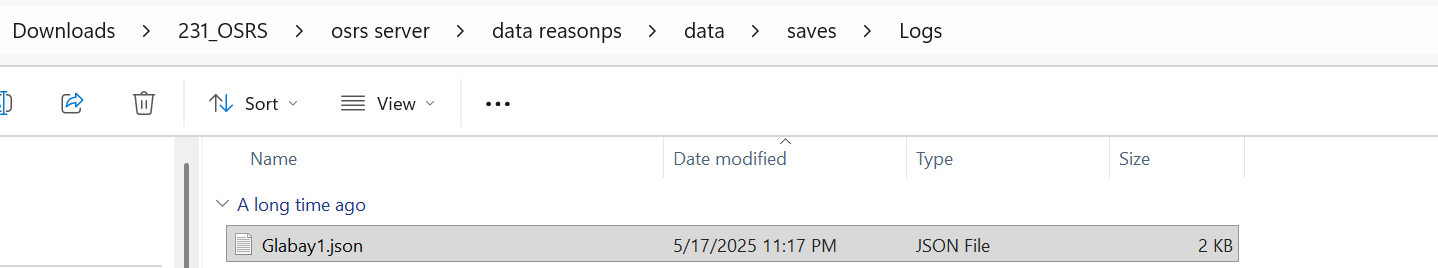
A save file in the logs data folder(this is for localhost use only) has the most recent user Glabay1.json
-
Log files, Gradle build files, and other digital artifacts may contain information that could be used to trace activity back to Glabay.
This is a recurring risk when developers have access to a full RSPS source code repository.
How a leak can affect other RSPS
Source leaks can affect other servers using the same codebase:
-
Clones appear quickly, damaging originality
-
Economies collapse if dupes or exploits are exposed
-
Player trust drops, especially for high-donation communities
-
Competitors gain unfair advantages
In a space where many servers rely on similar bases, one leak can expose vulnerabilities across multiple projects.
Security measures for RSPS owners
For more detail, read our RSPS server security guide.
The main steps are:
1. Vet Your Developers Thoroughly
-
Always research past work and reputation
-
Avoid giving full access immediately
-
Use staged permissions (dev → senior → core)
2. Lock Down Your Infrastructure
- Use a secured VPS environment
-
Restrict RDP access by IP
-
Disable unnecessary services
3. Separate Your Systems
-
Keep game server, webstore, and database isolated
-
Never store full source + credentials in the same place
4. Monitor Everything
-
Log file access and downloads
-
Track unusual behavior (large transfers, off-hour access)
-
Use alerts for suspicious activity
5. Use Version Control Properly
-
Private repositories only (GitHub/GitLab self-hosted preferred)
-
Limit cloning permissions
-
Audit commits regularly
Developer access and source security
Trusted insiders can pose a security risk.
Common causes of source leaks include:
-
Disgruntled developers
-
Internal disputes
-
Poor access control
0 Comments
Recommended Comments
There are no comments to display.
Please sign in to comment
You will be able to leave a comment after signing in
Sign In Now